
You still talk about the firewall as if it sits in front of the business. That sentence is how a lot of cybersecurity programs describe maturity: we bought threat-protection, we put it at the edge, we sleep. The operators hitting internet-facing Fortinet FortiGate and Palo Alto Networks GlobalProtect portals this month used a different sentence. They treated the appliance as a mailbox. Researchers tracking the campaign say more than 70,000 credentials came off exposed firewall and VPN gear, with follow-on attempts inside some of those networks. Leadership will ask whether you patched. Ask first whether the box already mailed your users’ passwords to someone who is currently running brute-force checks against every other portal you run.
Your Firewall Turned Cybersecurity Into a Password File
Edge appliances are sold as decision engines. Allow, deny, inspect, decrypt. In production they are also identity systems: SSL-VPN portals, local admin accounts, cached authenticators, API tokens for the orchestrator that pushes policy. A campaign that lives on those surfaces is a directory incident that happens to wear a network-vendor logo. You can patch the CVE tomorrow and still have an attacker holding last week’s export of users who were allowed to come in from hotels, clinics, and unmanaged laptops.

That is a bad look for any program that still reports “VPN uptime” as a security metric. Uptime on a public login prompt is availability for the attacker too. The interesting artifacts in this campaign are not the vendor names. They are the signs of reuse: operators who got a foothold and then tried to spend it. Stolen firewall credentials are rarely the end of the job. They are a boarding pass into management planes, config backups, and the identity provider you pointed the VPN at because you wanted single sign-on to feel convenient.
If your threat detection only watches the LAN behind the box, you are looking at the wrong side of the door. Successful SSL-VPN logins from new ASNs, fresh local admins, overnight config exports, and disabled logging are the incident. Packet drops on an unused rule are theater. Treat every internet-reachable management or VPN listener as a privileged identity store that happens to speak HTTPS. Then ask who has been reading it.
Assurance Lost at Every Hop You Outsourced
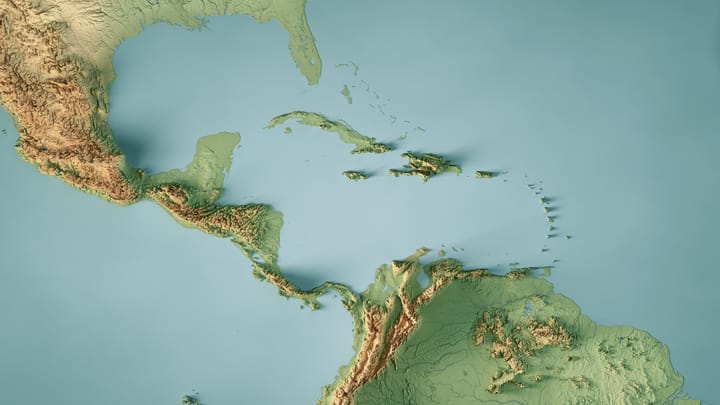
The same week, Dark Reading’s reporting on Caribbean operators put a regional label on a pattern you already know in your own change calendar. Exploits are moving faster than the paperwork, the patch windows, and the “we’ll get to that subnet in Q2” exceptions. When assurance lags, the first victims are the teams with thin benches and public services. The blast radius is not local. Payment processors, tourism platforms, managed DNS, and remote-access concentrators in one region become staging for sessions that terminate in yours. You do not need a Caribbean office to inherit a Caribbean failure. You need one vendor, one DNS hop, or one contractor VPN that still believes a green dashboard means the path is clean.
Call it cyber security without the slideware: you are only as current as the slowest trusted hop. Defense in depth that stops at your rack is a drawing. The drawing does not include the other organization’s overdue firmware, or the relay you never put on an asset list.
Cables and Tor exits fail the same custody test
London is proposing 14-year sentences for people who sabotage subsea cables, plus unlimited fines for ship owners, because the Submarine Telegraph Act 1885 still tops out around £1,000 and five years. That is a physical-layer admission. The paths your TLS sessions ride can be cut, bent, or tapped, and the legal regime until now treated that as a 19th-century telegraph nuisance. Hybrid operators already understood the economics. You should too. A cable you do not own is still part of your availability and confidentiality model, the same way a FortiGate you do own is part of your identity model.
Tor exit relays getting hijacked belongs on the same whiteboard. Teams still treat “anonymity network” as someone else’s problem, then wonder why a packet that egressed a “clean” VPN reappeared on a hostile hop. If you allow staff, researchers, or incident response tooling to traverse exits you do not control, you have volunteered a man-in-the-middle you will never see in the firewall GUI. Banks flagging rogue AI agents this week are tripping over a cousin of the same issue: an automated session that authenticates as a legitimate workflow. The common failure is custody of the path and the principal, not a shortage of logos on the rack.
Lock the Edge Like a Directory You Actually Own
Security hardening here is identity work. You are not “tuning IPS.” You are shrinking who can mint a session on a device that can rewrite your routes. Do the immediate work on the clock the attackers already used, then keep the ongoing controls in the same queue as Active Directory, not in the “network hygiene” backlog that never ships.
- Inventory every public listener that can authenticate a human or a token: SSL-VPN, device GUI, SSH, API, cloud-management connectors. If it answers from the internet, it is in scope for this campaign even if the hostname says “partner” or “DR.” Record last firmware, last admin login, and whether logging is actually leaving the box.
- Rotate on the assumption of theft. Every local admin password, RADIUS secret, LDAP bind account, API key, and cached user credential that touched those devices gets replaced. Kill standing VPN sessions. If you only reset the admin you remember, you missed the one they added at 03:12.
- Hunt before you declare clean. Pull success-after-failure bursts, logins from new countries or hosting ASNs, new local users, disabled syslog, and configuration export events. That is threat detection for an edge identity store. Packet counts will not save you.
- Get the admin plane off the public internet this week, not after the architecture review. Put operators through a jump path you control, with phishing-resistant MFA bound to the person, not to a shared “netadmin” token sitting in a spreadsheet. A VPN that is also the IdP for the rest of the company is a single vault with a welcome banner.
- Build incident response around “edge credential spend.” The first hour is revoke, isolate management, and compare running config to last known good. The first day is every downstream system that accepted those users: mail, SaaS, jump hosts, password vaults. Waiting for a vendor advisory to use the word “campaign” is how 70,000 logins become 70,000 other breaches.
- Keep defense in depth honest. A stolen firewall admin session should not be able to reset domain credentials, pull backups, or punch a persistent tunnel to a bulletproof host. Segment management, require a second control plane for identity changes, and alert when an edge device starts talking like a workstation.
If that list feels like directory operations, good. You have been doing network operations on an identity problem. The product still filters packets. The failure mode that just hit in bulk is people, secrets, and sessions living on a box you left reachable because “it’s the firewall.”
Frequently Asked Questions
- We patched FortiGate and GlobalProtect. Are we done?
- Firmware is necessary and it is not containment. Anyone who copied accounts before the patch still has a boarding pass until you rotate secrets, drop sessions, and prove no local users were added. Close the hunt when the logs and the identity provider agree, not when the version string looks current.
- Should we just shut off SSL-VPN?
- If you cannot put a phishing-resistant, inventory-backed control in front of it, exposing SSL-VPN to the world is volunteering a password oracle. Many teams can move remote access to a brokered path that never puts the device GUI on 443. If you must keep a portal, treat it like a domain controller: tiny user set, private management, and alerts on every new source.
- Why should a Caribbean outage or a UK cable law change my week?
- Because your users already authenticate across paths you do not patch. A delayed firmware cycle two providers away, or a physical cut on a route you never diagrammed, shows up as “weird VPN logins” in your console. Fold those hops into tabletop exercises the same way you fold a stolen firewall admin into incident response.
Sources
- Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials
- Why Caribbean Threats Cascade Into Global Cyber-Risk
- UK proposes 14-year jail terms for subsea cable saboteurs
- UK proposes 14-year prison terms for undersea cable sabotage
- In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuilding macOS Ransomware
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.