
South Africa asked for outside help after a cyberattack reached air traffic control, and investigators report a ransomware toolkit installed on at least one operational network. That detail should jump your change window. Aviation runs with thin safety margins, and a kit sitting on an ops segment is a live-fire cybersecurity problem for your incident response queue today. The same news cycle shipped roughly a dozen high-severity fixes in OpenSSL and another dozen in WolfSSL. If your threat detection still files those as a library ticket and an aviation curiosity, you have split one failure into two dashboards.
You do not need Johannesburg on your network map for this to apply. Any shop that still treats a perimeter firewall as threat protection for radar, radio, badge, or historian traffic is running the architecture ransomware kits prefer. Leftover TLS libraries with last quarter’s CVEs prefer it too.
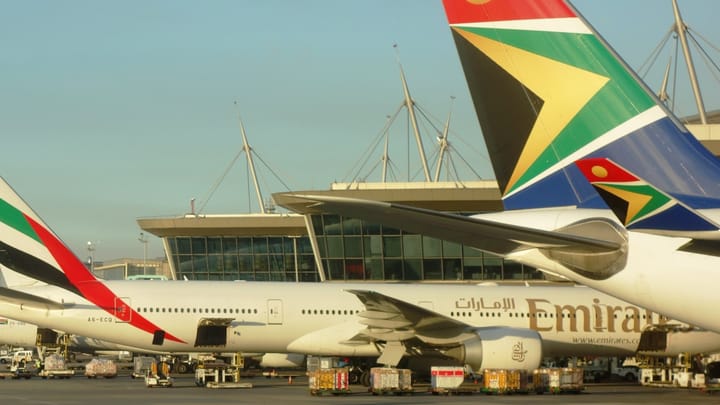
Ransomware Toolkit Confirmed on Operational ATC Segment
Dark Reading’s reporting is blunt: aviation infrastructure is taking more hits, air traffic systems are in the blast radius, and a ransomware toolkit made it onto an operational network. South Africa then asked for help. That sequence should rearrange how you rank safety-critical hosts. The kit on the ops box is the story. The press request is just the receipt.
Safety-critical networks fail in a boring way. Someone bridged a jump host, a vendor laptop, or a “temporary” management VLAN into a segment that was supposed to stay quiet. Defense in depth looked complete on the architecture diagram. East-west traffic still worked. Encryptors love working east-west paths. So do operators who need a shortcut at 2 a.m.
This is a bad look for any program that still grades cyber security by how pretty the airport or plant perimeter is. A WAN edge that drops scans does nothing once the toolkit is already inside the ops VLAN. Your users did not have to click a thing if the management plane was reachable from IT, if RDP and HTTPS admin listeners still accepted passwords, or if a contractor VPN dumped straight into the same subnet as production controllers.
Treat the South African incident as a copy of a pattern you already own. Ticket the question in writing: which of our networks could absorb a ransomware toolkit and still keep the safety function running? If the answer is “we’d restore from backup,” you have already accepted an outage on a system that does not get to go down for a restore window. ATC, rail, water, and plant networks share that constraint. The encryptor does not care which regulator you report to.
OpenSSL and WolfSSL CVEs Are Operational Cybersecurity Tickets
SecurityWeek’s roundup is the other half of the same week. Roughly a dozen vulnerabilities landed in OpenSSL. Roughly a dozen landed in WolfSSL. High-severity on both. These are not academic papers. They are the libraries under TLS handshakes, VPN concentrators, appliance admin portals, embedded devices, and a depressing number of vendor black boxes that still vendor-sign a private build you cannot grep.
WolfSSL shows up in firmware and constrained devices that never appear in your server CMDB. OpenSSL shows up in containers, load balancers, jump boxes, and that one Python service a contractor left running in 2022. A high-severity drop in both is a hunt across two supply chains. Waiting for the appliance vendor’s quarterly ISO is how last year’s library stays in production.
The real problem here is inventory. You cannot patch a .so you have not found. You cannot prove threat detection against a CVE if the only sensor watching that host is a syslog forwarder that died in March. Brute-force against an admin listener that still speaks TLS 1.2 with a stale WolfSSL is a Tuesday. The library advisory is the excuse to go look. Use it.
Do not merge this into a generic “crypto is hard” slide. Name the packages, the appliances, and the owners. If nobody owns WolfSSL in your environment, that is the finding. If OpenSSL versions diverge across three Linux estates and a fleet of vendor ADCs, that is also the finding. Patch lag on a TLS library is how an ops-adjacent box becomes the first foothold the next toolkit needs.
Segment Cuts, Library Inventory, and Management-Plane Locks
You can move this week without buying a platform. Immediate work is reachability and version evidence. Ongoing work is making both of those boring. Security hardening here is unglamorous: fewer paths, fewer admin listeners, known libraries, proven alerts.
- Export a list of every host and appliance that terminates TLS or ships a private OpenSSL or WolfSSL build, including jump boxes, vendor appliances, and “temporary” jump VMs.
- Default-deny east-west from IT user VLANs into safety-critical and ATC-class networks; put the management plane on its own path with MFA and a dedicated jump path.
- Prove lockout and brute-force controls on every admin listener, then patch or isolate anything still linked against the unfixed library.
After the list exists, walk the firewall rules that still allow “any any” between corporate and ops “for monitoring.” Monitoring can pull. It does not need to push ransomware. If a collector must speak into the ops segment, pin it to a named host, a named port, and a named identity. Recertify that path every quarter or it becomes a bridge.
Keep going. Snapshot library versions into the same ticket system you use for OS patching. When OpenSSL or WolfSSL ships a high-severity fix, the ticket should already know which images, containers, and firmware blobs need a rebuild. If your only signal is a vendor mailing list, you will learn about the next kit after encryption starts. Pair that with incident response drills that assume the first host is a jump box, not a workstation. Restore tests on safety-critical nets should include “can we run the safety function while this VLAN is dark,” not just “did the backup job finish.”
Defense in depth earns the name when the ops segment still functions after the IT domain is a crime scene. That is the bar. A colorful SOC dashboard is not the bar.
Crypto Discovery Still Absent From Incident Response Runbooks
Cloudflare’s engineering write-up on CryptoLabe is useful because it admits the unsexy part. They are building an internal tool to find cryptography in their own codebase, surface dependencies, and grind toward a full post-quantum migration by 2029. You can ignore the product branding. Keep the lesson. Migration dates are fiction until you can name every primitive, every library, and every caller.

Most incident response runbooks still start at “pull disk” and skip “which TLS stack was on this box.” That gap is how a ransomware toolkit on an ATC-class network and a two-dozen-CVE week in the crypto libraries feel unrelated. They are related. The kit needs a reachable host. The host needs a management plane. The management plane needs a TLS library. Your job is to make that chain short, logged, and expensive for an attacker.
Start the discovery where binaries actually live. Package databases, container SBOMs, firmware strings, and vendor support matrices. If a device cannot tell you its OpenSSL or WolfSSL version, treat it as expired until the vendor proves the build. Put that proof next to the segmentation diagram. When the next ATC-style incident hits the wire, you should already know which of your libraries were stale and which of your ops paths were still wide open.
Sources
- South Africa Seeks Help After Cyberattack Targets Air Traffic Control
- High-Severity Vulnerabilities Patched in OpenSSL, WolfSSL
- Using AI to chart a course for our post-quantum migration
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.