
An OpenAI employee planted a hidden recorder in an executive conference room, and most cybersecurity programs would never have seen it.
Abdulrahman Alfozan, 35, a Saudi national on the payroll, was arrested Friday and terminated, the FBI and the company said. He is charged with using an electronic device to intercept oral communications. The alleged plant sat in an executive space at OpenAI’s San Francisco offices, aimed at conversations leadership treats as secrets.
Your packet capture never had a chance.
This is a bad look for teams that score cyber security in tickets closed, CVEs burned down, and brute-force noise dropped at the firewall. A microphone with a badge does not beacon. It does not trip threat detection. It does not need a phishing kit or a zero-day. It needs unsupervised minutes with a power outlet and furniture nobody inventories.
Your Cybersecurity Stack Stops at Drywall
Defense in depth on the slide deck still ends at the NIC. Threat-protection tools grade mail and endpoints. Identity systems revoke SaaS tokens. None of that hears a whispered roadmap, an incident response tabletop, or a pricing fight you were foolish enough to hold in a glass room.
Microsoft just shipped more than 1,400 fixes, the fattest Patch Tuesday on record, with an in-the-wild Windows Shell Mark of the Web bypass and an Active Directory remote code execution flaw Redmond itself flags as more likely to be exploited. That queue will eat your week. It should. It will not tell you who sat alone in the boardroom at 9 p.m.
You will spend the next month arguing about change windows, Excel bugs, DNS roles, and whether Exchange content-conversion flaws are reachable in your shop. Those fights are real. Keep them in a ticket queue with owners. That motion is not coverage of human-placed hardware.

Unit 42’s dissection of an unsophisticated intrusion against a European bank is useful, and it becomes a trap if it is your only story about risk “inside” the network. Third-party traffic shows up in logs. Analysts hunt it because the graph lights up. Alfozan’s alleged kit was built to stay dark.
If your insider model is still a sysadmin dumping SharePoint, you are solving last year’s case. Physical interception belongs in the same privileged-access conversation as domain admin. Someone with a badge and a drawer full of USB chargers already has a path you do not monitor.
Treat Meeting Rooms as Privileged Assets
Start with the rooms, not the SIEM.
Immediate moves you can run this week without buying a product:
- Name every room where you discuss IR, credentials, mergers, customer incidents, or legal hold, then pull 90 days of badge history for after-hours and solo entry.
- Cut standing access. Sensitive rooms get named lists, logged doors, and a second person for after-hours work. Temporary badges die the day the visit ends.
- Ban personal electronics in those rooms, including wearables, and put the rule on the calendar invite. Collect phones in a box if the meeting is actually secret.
- Inspect furniture, power strips, conference phones, and odd USB gizmos before and after high-value meetings. Photograph a room baseline so new hardware is obvious.
- Stand up an incident response path for suspected audio interception: freeze the room, preserve the device, loop legal and HR, and assume every prior meeting in that space is burned.
Keep going after the first sweep. Recurring physical and RF checks, done by people who do not report to the occupants of the room, belong on a calendar you actually keep. Joiner, mover, and leaver tickets must kill room access the same hour they kill SSO. Vendors who “just need to fix the Polycom” get escorted, or they do not enter.
Classify the conversation, not just the file share. If a meeting cannot live in the notes system, it cannot live in a room with random drop-in rights and a bowl of dongles. Need-to-know on the invite list is security hardening. So is refusing to run board topics in a converted huddle space because the nice room is booked.
The CVE Flood Will Not Hear This
October 13 also ended the last year of paid updates for Windows Server 2012 and 2012 R2. Office 2021 went dark the same day. Those are loud, measurable, budgetable failures. A recorder is quiet until someone finds it, or until a competitor quotes your unreleased numbers back at you.
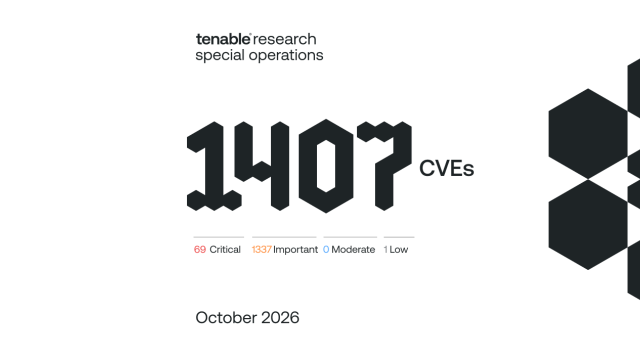
Operators love countable work. Fourteen hundred CVEs are countable. Firewall denies are countable. Brute-force source lists are countable. A late badge swipe into a dark conference room is countable too, if you staffed someone to care. Most of you did not.
Security hardening that ignores furniture is incomplete. You can patch Exchange, lock RDP, and still leak the merger in analog audio. Rank rooms the way you rank domain controllers: few, logged, dual-controlled, and treated as hostile the moment something looks off.
Patch the kernel. Sweep the table.
Sources
- Employee Arrested After Listening Device Found in OpenAI Conference Room, FBI and the Company Say
- OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room
- Microsoft Patches More Than 1,400 Security Flaws
- Microsoft’s October 2026 Patch Tuesday addresses 1407 CVEs (CVE-2026-96951)
- The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.