
Cybersecurity has become the word governments reach for when they want to move fast and skip the argument.
Call something a national security threat and suddenly the normal rules of debate, oversight, and proportionality don’t apply. A recent paper flagged by security researcher Bruce Schneier calls this “cybersecurity mission creep,” and once you see it, you can’t unsee it. Misinformation, child safety laws, antitrust fights, even journalist conduct disputes: reframe any of them as a cybersecurity issue and they instantly graduate from “important policy question” to “existential threat requiring urgent action.” That reframing isn’t free. It hands agencies exceptional powers to deal with problems that were never actually about network intrusions or stolen credentials.
Meanwhile, the stuff that actually fits the textbook definition of a cybersecurity failure gets nothing like that urgency.
The word moves fast. Real threats don’t
A security researcher found a flaw in Apple’s Hide My Email feature over a year ago. It’s still not fixed. He’s done waiting quietly, and honestly, so should the rest of us. This is a mainstream consumer privacy feature, built by one of the most resourced companies on the planet, sitting on a known weakness for twelve-plus months with no public timeline for a patch.
Compare that pace to how fast “cybersecurity” gets invoked when a government wants new surveillance authority or a platform wants to justify a takedown. The label is elastic when it’s convenient and oddly rigid, slow, bureaucratic, when it’s inconvenient.
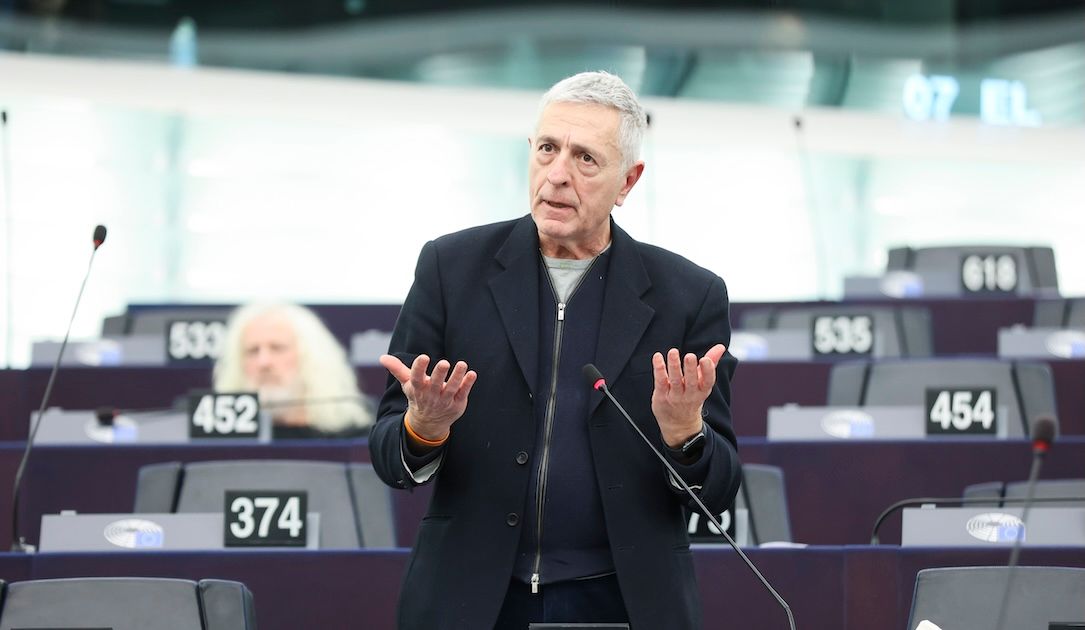
Then there’s the case of Stelios Kouloglou, a former member of the European Parliament committee that investigated abuses of commercial spyware. He was infected with Pegasus, according to researchers, not once but twice, while actively serving on the body meant to hold spyware vendors accountable. The person tasked with oversight became a target. If that doesn’t tell you something about how selectively the term “national security” gets applied, nothing will.
None of this is theoretical hand-wringing, either. The alleged Scattered Spider member extradited to the US this week is tied to more than 100 network intrusions and over $100 million in ransom payments. That’s a real cybersecurity crisis with a body count measured in businesses shuttered and hospitals disrupted. It got prosecuted the old-fashioned way: investigators, subpoenas, years of patient casework. No emergency powers required. Just competent, boring, sustained enforcement.
Boring is the whole point
PamStealer is a good example of the threats that actually deserve the word. Jamf Threat Labs found it impersonating Maccy, a legitimate open-source clipboard manager, distributed as a compiled AppleScript file that quietly checks system defenses before it siphons credentials. No political framing needed. It’s malware. It steals passwords. It’s a threat detection and incident response problem, full stop.
That’s the pattern worth noticing. The incidents that are genuinely about network security, stolen data, and compromised systems tend to get handled through unglamorous channels: patch cycles, malware research, extradition treaties, threat intel sharing. The incidents that get rebranded as cybersecurity for political leverage tend to arrive wrapped in urgency and short on due process.
Security teams don’t get to pick which framing wins in Washington or Brussels. But they do get to decide what their own defense in depth actually looks like, independent of whatever a headline calls it that week.
Build defenses that don’t care about the label
If you run infrastructure, the fix isn’t rhetorical. It’s operational. A few things worth doing regardless of what any given policy debate calls itself:
- Treat brute-force login attempts as a baseline threat, not an edge case. Rate-limit authentication endpoints and lock out or delay repeated failures automatically.
- Segment your network so a compromised endpoint, whether from a stealer like PamStealer or a phished credential, can’t reach everything else.
- Keep firewall rules and management interfaces off the public internet by default. Most large intrusions still start with an exposed admin panel.
- Log authentication events somewhere attackers can’t reach or delete, so incident response actually has something to investigate after the fact.
- Patch based on what’s actually being exploited, not on vendor severity scores or news cycle attention.
- Review third-party and partner access regularly. Microsoft’s recent push to vet its own partner ecosystem is a reminder that supply chain trust needs periodic re-certification, not a one-time approval.
Security hardening works the same whether or not a politician decides to call your problem a crisis this quarter.
Curiosity helps too. Talos researcher Bill Largent made the case this week that pattern recognition, the same instinct that makes someone good at board games, is a defender’s most useful trait. That’s a better foundation for a security program than chasing whatever term is trending in a policy hearing.
The next time someone slaps “cybersecurity” on a policy fight that has nothing to do with intrusions or stolen data, ask what actual technical problem it’s supposed to solve. Usually there isn’t one. The real cybersecurity problems, the Pegasus infections, the unpatched Apple bugs, the ransomware crews working extradition dockets, don’t need a rebrand. They need people who show up and do the unglamorous work.
Sources
- Cybersecurity Mission Creep in the US
- Apple’s Hide My Email doesn’t hide it very well
- Spyware found on phone of European Parliament member probing it
- Alleged Scattered Spider Hacker Extradited to US
- PamStealer Uses Fake Maccy Sites and PAM Checks to Steal Mac Login Passwords
- Catan and Mouse
- Improving security posture across the Microsoft partner ecosystem
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.