
GitLab’s threat model apparently assumed that anyone who could log in could be trusted not to read a diff. That’s the kind of assumption that ages like milk, and this week it curdled publicly. A researcher published a working proof-of-concept that turns an ordinary, no-special-privileges GitLab account into command execution as the git user, and the trigger is committing two crafted Jupyter notebooks and asking the server to show you the difference between them. No admin rights. No CI runner access. No victim has to click anything. Just a login and a diff request, and that’s the kind of low bar that should worry anyone thinking seriously about cybersecurity for their internal developer tooling, not just their public-facing apps.

What Actually Happened, In Plain English
Jupyter notebooks are JSON files that mix code, output, and rendered content. GitLab, like a lot of platforms, tries to render notebook diffs nicely so you can see what changed without squinting at raw JSON. Somewhere in that rendering pipeline, on unpatched self-managed GitLab 18.11.3, there’s a path that lets a crafted notebook pair smuggle in something the server executes instead of just displaying. The researcher, Yuhang Wu, didn’t need to compromise an admin account or find a way onto a CI runner, the two usual chokepoints defenders assume protect them. He just needed an account with commit access, which on most GitLab instances describes half the engineering org and a good chunk of contractors.
That’s the part that should sting. Most breach post-mortems involve either a phished credential with elevated access or a misconfigured pipeline with too much trust baked in. This one requires neither. It’s a reminder that “authenticated user” is doing a lot of unexamined work in a lot of security models, and that work doesn’t hold up when the authenticated user is the attacker.
Why This Is a Bigger Cybersecurity Problem Than the Patch Notes Suggest
Every org with self-managed GitLab has already made a trust decision, whether they meant to or not: anyone who can push code can be trusted with the underlying server. That decision usually goes unexamined because it feels obviously fine. Developers aren’t the threat, right? Except developer accounts get phished, contractor accounts get sold, and disgruntled employees exist. When the barrier between “committed a file” and “ran a command as git” is this thin, you’re not defending a perimeter anymore, you’re defending against your own user base, and that changes what threat detection needs to look for.
This is exactly the blind spot that defense in depth is supposed to cover, and exactly the blind spot that keeps not getting covered in practice. Perimeter firewall rules, brute-force lockouts, MFA on the login page: none of it touches a vulnerability that fires after a legitimate login, inside a feature nobody thought to threat-model because it’s “just a diff viewer.” The tools that render your source-of-truth code repository need the same scrutiny as your internet-facing services, because functionally, for anyone with an account, they are internet-facing services.
Rockwell’s Arena Bug Says This Isn’t a GitLab Problem, It’s a Pattern
Same week, different vendor, same shape of failure. Rockwell Automation patched code execution flaws in Arena, its industrial simulation software, after a researcher detailed how an attacker could exploit them against manufacturing and process organizations. Arena isn’t internet-facing. It’s a desktop application engineers use to model production lines. The attack path runs through malicious project or model files that an engineer opens because a colleague, a vendor, or someone posing as either sent it to them. No firewall rule stops that, because the file arrives through email or a shared drive, not through an open port.
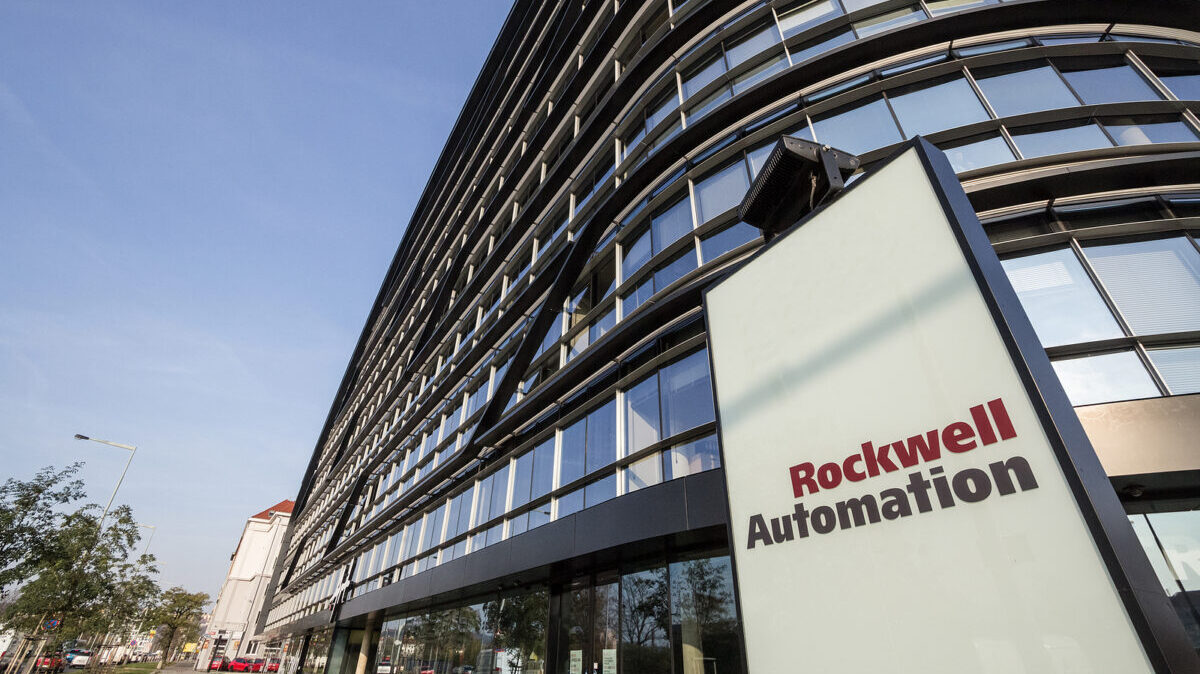
Put these two next to each other and the pattern is hard to miss. Security teams pour resources into hardening the network edge and the login page, and meanwhile the software engineers and operators actually use all day, the code host, the simulation tool, the CAD package, sits several rungs down the priority list. SecurityWeek’s roundup the same week noted Siemens switch flaws, a Russian espionage campaign against Zimbra webmail, and a ransomware extortion attempt against rail manufacturer Stadler, three more examples of attackers going after the software running behind the perimeter rather than the perimeter itself. Add in reports of roughly 400 outstanding flaws across the Linux kernel and you’ve got a full week of evidence that the stuff your engineers open, run, and trust every day deserves the same posture as anything sitting on the open internet.
What To Actually Do About It This Week
None of this requires exotic tooling. It requires treating internal engineering software like the attack surface it is, which mostly comes down to discipline you already know how to apply elsewhere.
- Patch self-managed GitLab now if you’re running 18.11.3 or earlier, and stop assuming SaaS-hosted instances are automatically out of scope, verify your version and patch status directly.
- Audit who actually needs commit access versus who has it by default. Fewer accounts that can trigger the vulnerable path means fewer accounts an attacker needs to compromise.
- Apply security hardening to the GitLab host itself: run it with least privilege, isolate it from production credentials, and make sure the git service account can’t reach anything it doesn’t strictly need.
- Treat engineering desktop software, Arena, CAD tools, notebook viewers, as part of your patch management cycle, not an afterthought behind server and browser patching.
- Build detection for anomalous behavior from the git service account or notebook rendering process, not just failed logins and brute-force attempts. Threat detection tuned only for credential abuse misses exactly this class of bug.
- Make sure your incident response plan actually names who owns internal dev tooling, because right now that ownership gap is where these bugs go unpatched the longest.
None of this is glamorous. It’s also exactly the kind of unglamorous work that would have mattered here, since the GitLab bug requires no cleverness to exploit once you know the trick, only a patch level that hasn’t caught up.
Sources
- Researcher Publishes GitLab RCE PoC Letting Authenticated Users Run Commands as Git
- Rockwell Patches Code Execution Flaws in Arena Simulation Software
- In Other News: Dolphin X AI-Powered Malware, Car Anti-Theft Device Hack, 400 Linux Kernel Flaws
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.