
Two Windows bugs that raise a local account to SYSTEM are already being exploited. Your change board just inherited nearly a thousand other tickets in the same drop. That mismatch is the bill for this week’s cybersecurity calendar: every extra day you spend proving 972 low-priority fixes is another day someone spends as SYSTEM on the two that already shipped as working exploits.
Microsoft’s September 2026 updates plug at least 974 holes across Windows and adjacent products, the largest single patch batch the company has ever shipped. July’s previous record sat at 664. Security teams did not magically grow a third of extra testers, lab VMs, or maintenance windows between those two Tuesdays.
Record Volume Turns Patching Into Guesswork
SANS counts 973 vulnerabilities this month, 113 of them rated critical. None of the bugs were publicly disclosed before Patch Tuesday. Two were already in use. Dark Reading notes Microsoft also flagged 58 more as likelier to be exploited. SecurityWeek puts 20 in the potentially wormable bucket. You cannot treat those four numbers as one queue.
Microsoft issued updates to plug at least 974 security holes in Windows and other software, by far its biggest single patch batch ever.
Brian Krebs reported that artificial intelligence is speeding how fast Microsoft finds defects. The human side of the work did not get the same boost. Testing Group Policy, print paths, DNS, Kerberos, and line-of-business clients still burns calendar time. So does rolling a bad fix out of production. Volume here is a scheduling attack on your own process.
Elevation of privilege made up about 45 percent of the batch. Remote code execution sat near 27 percent. A lot of the rest is noise your ticket system will still insist you acknowledge. If your cyber security program grades success by percentage of CVEs closed, this month will look like a failure even if you nail the two live escalations and the wormable network services first.
A perimeter firewall does not rank this list for you. Neither does a brute-force dashboard on the VPN concentrator. Those controls matter, and they are the wrong lens for a local SYSTEM race already in the wild. Threat detection that only watches the edge will miss the Update Stack and ALPC paths that start after a foothold exists.
Unpatched Services Keep Handing Out SYSTEM
Start with the two that already escaped the lab. CVE-2026-81963 is a Windows Update Stack elevation of privilege, scored 7.8, exploited as a zero-day. Microsoft describes a link-following flaw that lands SYSTEM. Tenable notes seven Update Stack privilege bugs have been patched since 2022; this is the first known to be exploited in the wild. CVE-2026-85880 hits Advanced Local Procedure Call the same way: 7.8, SYSTEM, already used. ALPC had gone quiet on Patch Tuesday for more than three years. It is quiet no longer.
Then look at the services that turn one host into many. CVE-2026-69730 is a Windows DNS Server remote code execution bug at 9.8, unauthenticated, use-after-free, rated Exploitation More Likely. Eight other DNS RCEs shipped in the same drop with weaker exploitability notes. CVE-2026-69676 is a critical Kerberos remote code execution path that leans on capture-replay. Remote Desktop Services picked up CVE-2026-69525, another 9.8 RCE Microsoft also marked more likely, plus a cluster of related RDS fixes. SANS also flags critical RCEs in Skype for Business, MSMQ, and Routing and Remote Access.
Those names should already sit on your internet-exposure and jump-server maps. RRAS, MSMQ, aging Skype for Business pools, and DNS listeners are classic “we still need it for one vendor” leftovers. Leave them unpatched while you regression-test Paint and Xbox Gaming Services and you have donated a wormable lane. Defense in depth only works if the inner layers get the first maintenance window, not the last.
Exchange is in this batch too. CVE-2026-69380 is a missing-authorization elevation that lets a low-privilege mailbox user reach other mailboxes. Microsoft rates exploitation less likely, which is not the same as “ignore until October.” Mail identity is still incident response fuel. Treat it as a directory-adjacent problem, not a CVSS trivia item.
Cybersecurity Triage Beats a Full Sweep This Week
You will not finish 974 patches before attackers reuse the two they already have. Rank work by evidence of exploitation, then by unauthenticated reachability, then by privilege gained. Security hardening this month is a sequenced list, not a green dashboard.
Do this immediately:
- Confirm the September cumulative is approved for domain controllers, DNS servers, RDS gateways, RRAS, MSMQ hosts, Skype for Business, and anything that still speaks those protocols. Patch those rings first, with a documented exception only if a named business process blocks the reboot.
- Hunt for CVE-2026-81963 and CVE-2026-85880 behavior now: unexpected SYSTEM children from Windows Update components, odd ALPC activity after a non-admin logon, and new local admins that no change ticket explains. Feed those hunts into incident response before the “we patched last night” meeting.
- Pull internet and partner exposure for DNS, RDP, RRAS, and message-queuing endpoints. If a service exists only because nobody deleted it, delete it. Threat-protection products will not compensate for a listening wormable service you forgot you owned.
- Freeze low-value desktop CVEs out of the emergency window. Office, media codecs, and consumer Xbox components can ride the normal ring. Do not let them steal DC reboot slots.
Keep doing this after the emergency window closes. Rebuild your exploitability ranking every Patch Tuesday from Microsoft’s index plus your own asset inventory, not from CVSS alone. Track time-to-patch for exploited and “more likely” items as a separate SLA from bulk desktop compliance. Exercise the rollback path on a staging DC and a staging DNS server so a bad fix does not become an unplanned outage that teaches the business to delay next month. Log who approved each deferral, with an expiry date, so deferred wormable services cannot hide in a spreadsheet until they are a breach report.
This is a bad look for any program that still sells leadership a 30-day patch SLA as if volume were constant. July’s 664 already stretched that fiction. September broke it. Your testers are the constraint. Spend them on SYSTEM and on the services that replicate code across the estate. Everything else can wait in a numbered queue that you actually review.
Sources
- Microsoft Plugs Nearly 1,000 Security Holes
- September 2026 Microsoft Patch Tuesday
- Microsoft Patches Record 974 Vulnerabilities, Including Two Exploited Zero-Days
- Patch Tuesday Sets Another Record With 974 CVEs
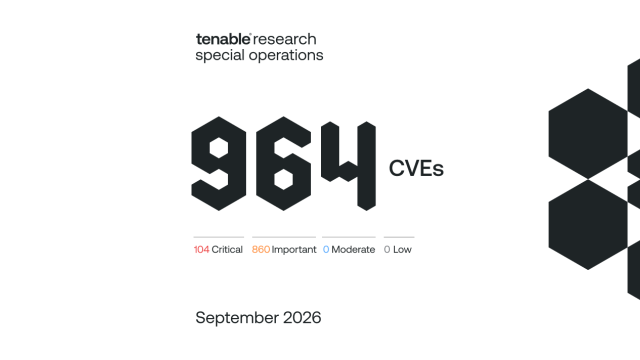
- Microsoft’s September 2026 Patch Tuesday addresses 964 CVEs
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.