
More than 80,000 AI relay servers now sit between users in China and the frontier models your labs, vendors, and API bills are supposed to keep exclusive. Dark Reading reports those relays mask identities while people reach cutting-edge large language models, probably to clone them. For a cybersecurity team that still scores risk by source country, that is months of training spend walking out as ordinary HTTPS. You already paid for the output. Someone else is keeping the copy.
The sessions look clean. Tokens validate. Latency is fine. Your threat detection never gets a malware hash because there is nothing to detonate. The loss is the prompt stream, the sampled weights, and the distillation set you never labeled as an exfil event. Key rotation will not buy that moat back. Rotation stops the next pull. The student model is already trained.
Relays Hide the Buyer and Ship the Weights
A relay is a costume. The client your gateway sees is a hop in a friendly region, on a bland ASN, with a user-agent that matches a paying developer. Behind it, Dark Reading says, is a farm large enough that 80,000 servers is the published count, not a rounding error.
More than 80,000 AI relay servers are helping users in China mask their identities while they access cutting-edge large language models, probably to clone them.
Read that as an operations problem. Your firewall still has a geo rule. Your WAF still has a rate limit per IP. A relay farm spreads calls, rotates egress, and keeps every individual address under the brute-force and abuse thresholds you tuned for noisy scanners. A few hundred active hops at a time, each politely under quota, still drains a frontier API.
This is a bad look for anyone selling AI access control as a country block. The real problem here is that frontier-model theft does not show up in yesterday’s incident response runbook. You have playbooks for ransomware. You have playbooks for leaked tickets. You rarely have a playbook for a stranger distilling your model through a month of legal-looking API use.
If you expose a commercial LLM, an internal assistant with web tools, or a partner-facing model endpoint, you are in the blast radius. Relays need a key, a quota, and patience. Staff keys on a corporate card, vendor wrappers, and “temporary” eval tokens are enough. The clone does not need your brand. It needs your capability.
A Bluetooth Pair Turns Staff Into Bystanders
The same week’s wearable tests make the identity failure physical. Malwarebytes reports that some cheap smart glasses can be hijacked over Bluetooth, exposing photos, videos, and personal data. That is a meeting recorder you issued, or a gadget a VP bought, now answering to whoever won the pairing race.
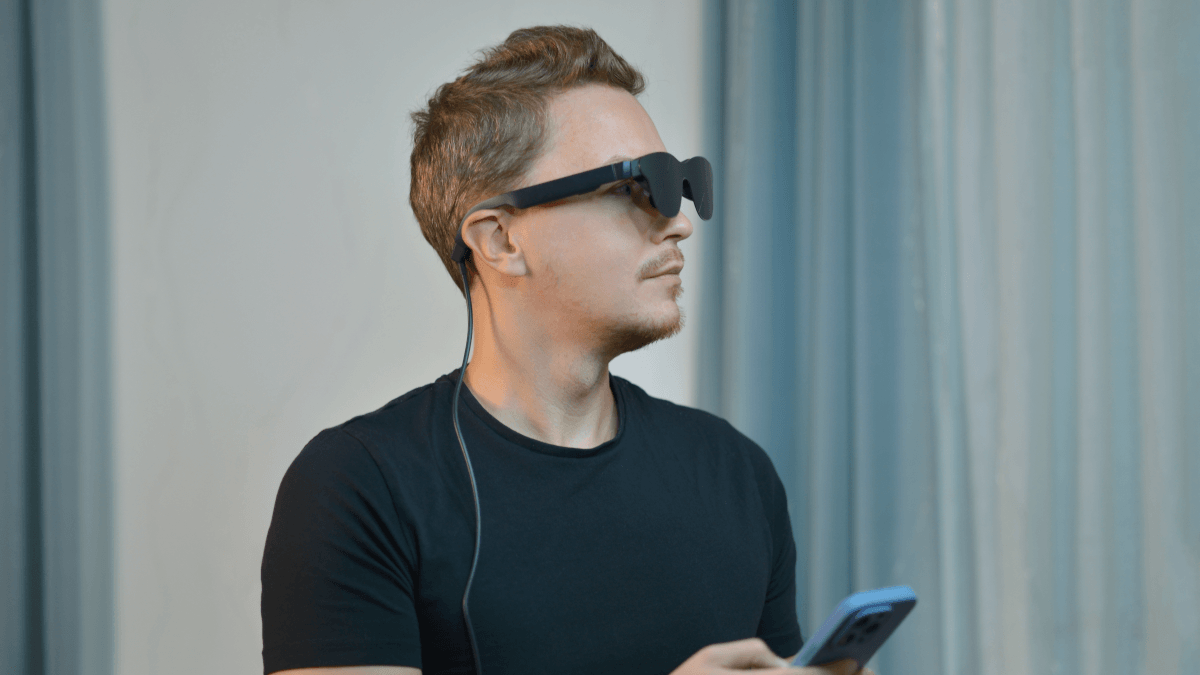
You already argue about phones in secure spaces. Glasses sit on a face, they cache what the wearer saw, and cheap firmware often treats the first Bluetooth friend as family. A nearby attacker skips your IdP and takes the camera roll that walked through the lab.
Network identity and device identity failed in the same news cycle. Relays hide who is calling your model. A hijacked wearable hides who is standing in your building. Threat-protection that assumes the authenticated object is a person you met will file both as traffic.
Treat that as one control gap. Your cyber security program keeps buying tools that inspect payloads. The caller is the payload that never got inspected. Until you bind a human or a workload to the session, defense in depth is a stack of sensors watching a costume.
Cybersecurity Hardening Starts With Binding the Caller
The farm stays up. Your job is to make cloning expensive, and to make a hijacked wearable useless on your sites. Do the ugly work this week, then keep it on a calendar.
- Pull 90 days of AI-gateway and LLM-provider logs and group by billing account, key, ASN, TLS fingerprint, and prompt volume. Flag accounts whose egress ASN jumps across regions while the human owner does not. That is relay-shaped even when every call authenticates.
- Freeze issuance of long-lived API keys. Move model access to short-lived, SSO-bound or workload-identity tokens with per-key quotas that page a human. Shadow SaaS keys on corporate cards count. Inventory them like production secrets.
- Add an incident response trigger for model-theft suspected: evaluation-style query batteries, sudden multilingual diversity, systematic capability probes, and weight-adjacent extraction patterns. Successful auth is not a reason to drop the ticket.
- Disable open pairing on any managed wearable. Ban unmanaged smart glasses from labs, NOCs, and board sessions until you can prove the Bluetooth stack. Rehearse wearable loss the way you rehearse laptop loss; photos from a badge line are spill data.
- Keep hunting relay-like behavior the way you hunt command channels: stable accounts, unstable paths, and success where you expected scarcity. Legal and comms should already treat a cloned model as a loss event, not a branding dispute after the student model ships.
None of this needs a new product category. It needs owners. If nobody owns who is allowed to talk to the model, and who is allowed to record the room, your stack will keep filing both as growth.
Sources
- Relays Are Masking Chinese Access to Frontier AI Models in the US
- Some cheap smart glasses are a security disaster
Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.

Take Control of Your Server Security
Don't let brute-force attacks slow you down. Try IPBan Pro risk-free for 30 days.
Secure. Automated. Lightweight.